SSOGEN / Learn / Open Source SSO: Your Options and When You Outgrow Them
SSOGEN
Open Source SSO: Your Options and When You Outgrow Them
Keycloak, authentik, CAS and the modules and proxies around them, sorted, with the points where a team outgrows a pile of parts.
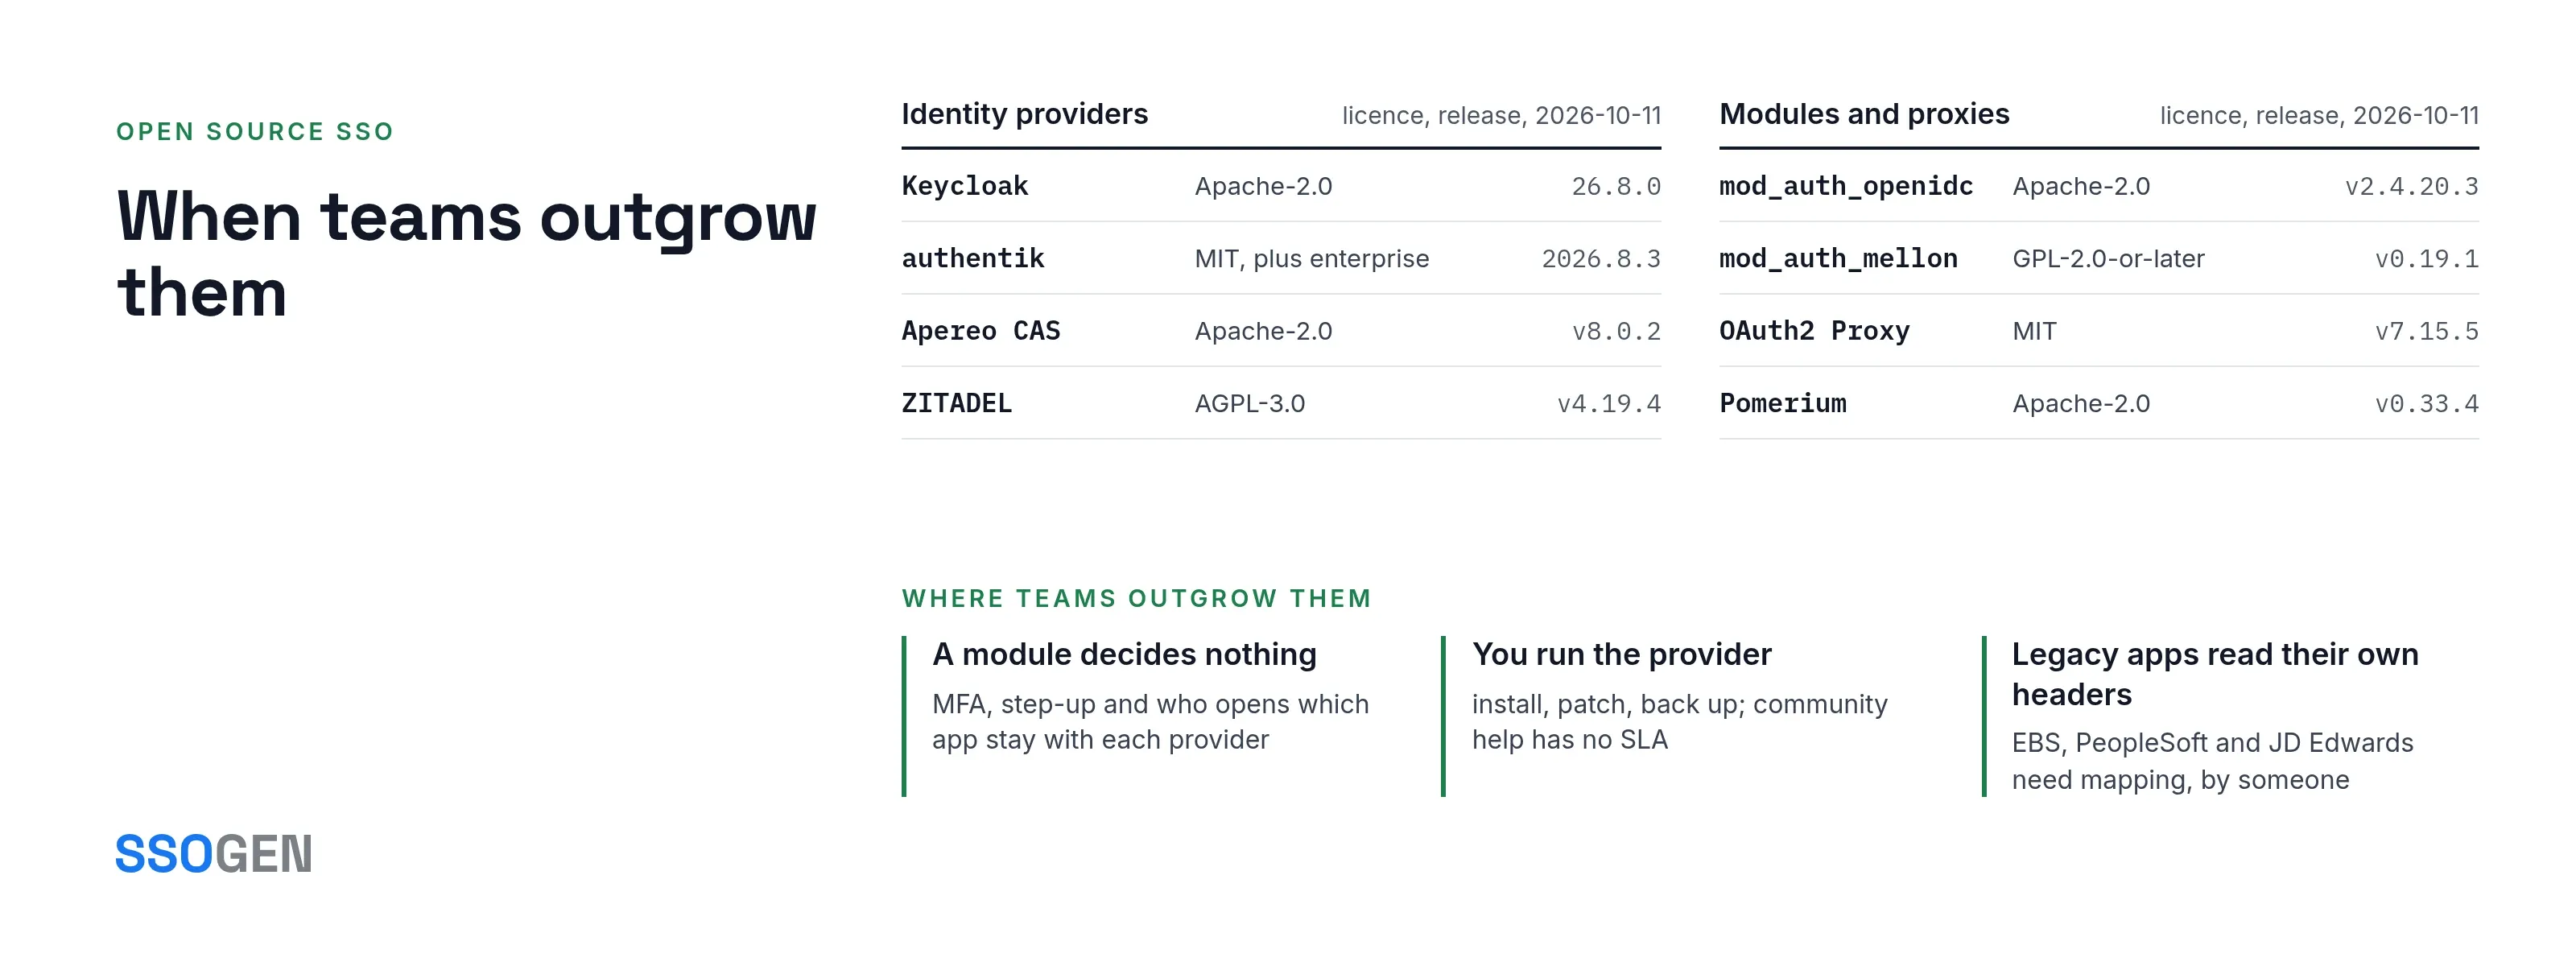
Open source SSO is a real option, and for many teams the right one. Every project below publishes its source, and each had a release or commit in the last six months when we read it (2026-10-11).
First, pick the kind you need:
- An identity provider or server stores or federates users and decides who can sign in.
- A module or proxy sits in front of one application and hands the sign-in to a provider.
Most estates end up with one of each. The tables below list both kinds with license, latest release and last commit, followed by the points where teams outgrow them.
Every project fact here comes from the project’s own README, documentation or GitHub repository data, read on 2026-10-11. Stars and activity change daily, so treat the dates as a snapshot.
Identity providers and servers
| Project | What it is | Protocols (per the project) | License | Latest release | Last commit | Good fit |
|---|---|---|---|---|---|---|
| Keycloak | Identity and access management server (Java) | OpenID Connect, OAuth 2.0, SAML 2.0 | Apache-2.0 | 26.8.0 (2026-10-01) | 2026-10-10 | Apps that already speak SAML or OIDC; teams that can operate it |
| authentik | Identity provider (Python) | SAML, OAuth2/OIDC, LDAP, RADIUS | MIT, with an enterprise directory under a separate license | 2026.8.3 (2026-09-17) | 2026-10-10 | Self-hosted from lab to cluster; paid enterprise tier exists |
| Authelia | Authentication and authorization portal (Go) that works with reverse proxies | OpenID Connect 1.0, OAuth 2.0 | Apache-2.0 | v4.39.28 (2026-09-17) | 2026-10-10 | Reverse-proxy setups that need a portal with two-factor |
| Shibboleth Identity Provider | Single sign-on server from the Shibboleth Consortium | SAML | Apache-2.0 | 5.2.3 (2026-06-18) | Not on GitHub | Federations and universities with complex attribute release |
| Apereo CAS | Identity provider and SSO server (Java) | CAS, SAML 1 and 2, OAuth 2.0, OpenID Connect, WS-Federation | Apache-2.0 | v8.0.2 (2026-09-26) | 2026-10-11 | Higher education and anyone who needs the CAS protocol |
| SimpleSAMLphp | PHP application for authentication | SAML 2.0 as SP and IdP; also CAS, OpenID Connect, WS-Federation, OAuth | LGPL-2.1 | v2.5.3.1 (2026-08-09) | 2026-09-29 | PHP shops that need SAML in a small footprint |
| Dex | Federated OpenID Connect provider (Go) with connectors to LDAP, SAML and others | OpenID Connect | Apache-2.0 | v2.46.0 (2026-10-07) | 2026-10-07 | Kubernetes and apps that want one OIDC front for many directories |
| ZITADEL | Identity and access management system (Go) | OpenID Connect, SAML 2.0 | AGPL-3.0, with Apache-2.0 and MIT exceptions for some directories | v4.19.4 (2026-10-01) | 2026-10-09 | Multi-tenant SaaS builders who accept the AGPL |
| Ory Kratos and Hydra | Kratos: headless identity management. Hydra: OAuth2 and OpenID Connect provider (both Go) | OAuth 2.0, OpenID Connect (Hydra); Kratos lists OIDC and SAML | Apache-2.0 | v26.2.0 for both (2026-03-20) | 2026-07-29 for both | Developers composing their own login UI |
Modules and proxies that add SSO to an existing app
| Project | What it is | Protocols (per the project) | License | Latest release | Last commit | Good fit |
|---|---|---|---|---|---|---|
| mod_auth_openidc | Apache 2.x module (C), OpenID Connect and FAPI 2 relying party | OpenID Connect 1.x, FAPI 2.x | Apache-2.0 | v2.4.20.3 (2026-09-01) | 2026-10-01 | Apache sites against an OIDC provider |
| mod_auth_mellon | Apache module (C), SAML 2.0 service provider | SAML 2.0 | GPL-2.0-or-later, with an OpenSSL exception | v0.19.1 (2024-07-16) | 2026-10-09 | Apache sites against a SAML IdP |
| Shibboleth Service Provider | Service provider that integrates with web servers | SAML | Apache-2.0 | 3.6.0 (2026-09-14) | Not on GitHub | Federations that use Shibboleth metadata |
| mod_auth_cas | Apache module for an Apereo CAS server | CAS v1 and v2, SAML | Apache-2.0 | v1.3 (2026-05-27) | 2026-05-27 | Sites already running CAS |
| OAuth2 Proxy | Reverse proxy or middleware (Go) | OAuth2, OIDC | MIT | v7.15.5 (2026-10-01) | 2026-10-01 | Putting a login in front of one app through a proxy |
| Vouch Proxy | SSO for Nginx through its auth_request module (Go) |
OAuth, OIDC | MIT | No GitHub release; latest tag v0.50.0 (2026-09-27) | 2026-09-27 | Nginx users protecting many sites at once |
| Pomerium | Identity and context-aware reverse proxy (Go) | Uses your identity provider | Apache-2.0 | v0.33.4 (2026-10-02) | 2026-10-09 | Clientless access to internal apps without a VPN |
Release and commit dates are from the GitHub API for each repository (default branch) and the Shibboleth download pages, read 2026-10-11. The protocol and description columns are the project’s own wording in its README or site.
Check the repository before you copy a tutorial
Old tutorials point to old repositories. The clearest case is mod_auth_mellon.
| Repository | State | Latest release | Last push |
|---|---|---|---|
| Original UNINETT repository | Archived on GitHub | v0.14.2 (2019-03-21) | 2020-01-28 |
latchset organization |
Under active maintenance, per its README | v0.19.1 (2024-07-16) | 2026-10-09 |
The project lives on under the latchset organization. Its README says it “is under active maintenance” and “was forked from the original Uninett repository when Uninett chose to retire their version”.
The name is the same and the repository is different. Check which one a guide tells you to build.
Support is the second point to check. Apereo’s CAS support page says CAS is “supported primarily by an open and friendly community”, with no SLAs and no guarantees. Paid support comes from Apereo’s commercial service providers.
mod_auth_openidc’s README says builds for Oracle HTTP Server, IBM HTTP Server and some other systems are available under a commercial agreement. An open source license does not always mean the exact build you need is free.
When teams outgrow them
None of these is a flaw. They are the points where a project’s own documentation stops, and you either build the missing part or buy it.
- A module or proxy decides nothing about who can sign in. The mod_auth_mellon README says the module authenticates the user against a SAML 2.0 IdP, and the mod_auth_openidc README says it relays authentication to a provider. Multi-factor prompts, step-up and who can open which app are the provider’s job. Across several Apache sites, policy stays split among their providers.
- You run, patch and back up the provider. Keycloak, Authentik, CAS and the rest are software you operate. Apereo’s CAS support page says plainly that community help has no SLA, and points to commercial providers for paid support. A support contract, where one exists, is one per project.
- The license changes the plan. ZITADEL is AGPL-3.0 for most of its code, authentik keeps an enterprise directory under a separate license, and mod_auth_mellon is GPL. Check each against how you will deploy or embed the software.
- Legacy applications do not read standard claims. mod_auth_openidc passes claims to the application as headers or environment variables, with the claim prefix
OIDC_CLAIM_by default (sample configuration, read 2026-10-11). Oracle E-Business Suite, PeopleSoft and JD Edwards look for their own header names, which the README and sample configuration do not describe. Someone has to map them. - Support can fall between two projects. Keycloak’s guides for mod_auth_openidc and mod_auth_mellon each say Keycloak provides no official support for the module (read 2026-10-11). A problem lands in the gap.
Where SSOGEN fits
SSOGEN is commercial software, not open source. It covers the points above in one product, supported by the team that builds it and in production since 2016:
- A complete identity provider for any application that speaks SAML 2.0 or OpenID Connect.
- A Web Agent, an Apache and Oracle HTTP Server module. In SSOGEN mode it needs no license key and applies the same sign-in, MFA and step-up policy as every other application. The standalone SAML and OpenID Connect modes need a license key from SSOGEN.
- The Oracle application profile, with which the agent upper-cases the user name and sends the legacy headers Oracle applications read.
- A Gateway with an App Proxy for apps that cannot host a module.
If your apps already speak SAML or OpenID Connect and you have staff to run Keycloak, Keycloak does that job well.
SSOGEN is the stronger choice for Oracle ERP behind Apache, one place for policy, MFA and the audit log, and a vendor to call.
For those cases see the Apache module comparison, the Keycloak alternative page, and how to run your own identity provider. For side-by-side pages see the comparison hub.
Questions people ask
What is open source SSO?
Is Keycloak open source SSO?
Which open source SSO works with Apache?
Is open source SSO free?
Where to go next
- Behind Apache. Start with the Apache SSO module comparison if your app sits behind Apache.
- Running Keycloak. Read about the Keycloak alternative if you already run Keycloak.
- Apps that cannot redirect. The Web Agent and Gateway pages show how SSOGEN covers applications that cannot redirect to a provider.
- Side by side. The comparison hub lists side-by-side pages.
- Back. Back to Learn.
Sources, all read 2026-10-11: GitHub API and READMEs for each repository named above, Keycloak, Keycloak guide for mod_auth_openidc, Keycloak guide for mod_auth_mellon, Apereo CAS support, Shibboleth Identity Provider documentation, Shibboleth Service Provider documentation, Shibboleth downloads, SimpleSAMLphp, mod_auth_mellon README, mod_auth_openidc README. The mod_auth_openidc sample configuration was also read 2026-10-11.
About this guide. SSOGEN Corporation prepared this page from each project’s public README, documentation and repository data, last read on 2026-10-11.
We took care to be accurate, but projects, licenses and releases change, and we may have misread or missed something, so some statements may be wrong or out of date. This page is for general information only and comes without any warranty.
SSOGEN is not responsible for errors, omissions or decisions made from it. Check each project’s own pages and test the software yourself before you decide. If you see a mistake, tell us and we will correct it.
Keycloak, authentik, Authelia, Shibboleth, Apereo, CAS, SimpleSAMLphp, Dex, ZITADEL, Ory, mod_auth_openidc, mod_auth_mellon, mod_auth_cas, OAuth2 Proxy, Vouch Proxy, Pomerium, Apache, Nginx, Oracle E-Business Suite, PeopleSoft, JD Edwards, Oracle HTTP Server and IBM HTTP Server are names or trademarks of their respective owners.
SSOGEN is an Oracle partner, but Oracle has not reviewed or endorsed this page. The owners named are not affiliated with, endorsed by or sponsored by SSOGEN.