SSOGEN / Oracle EBS Okta SSO
Integration
Oracle EBS Okta SSO
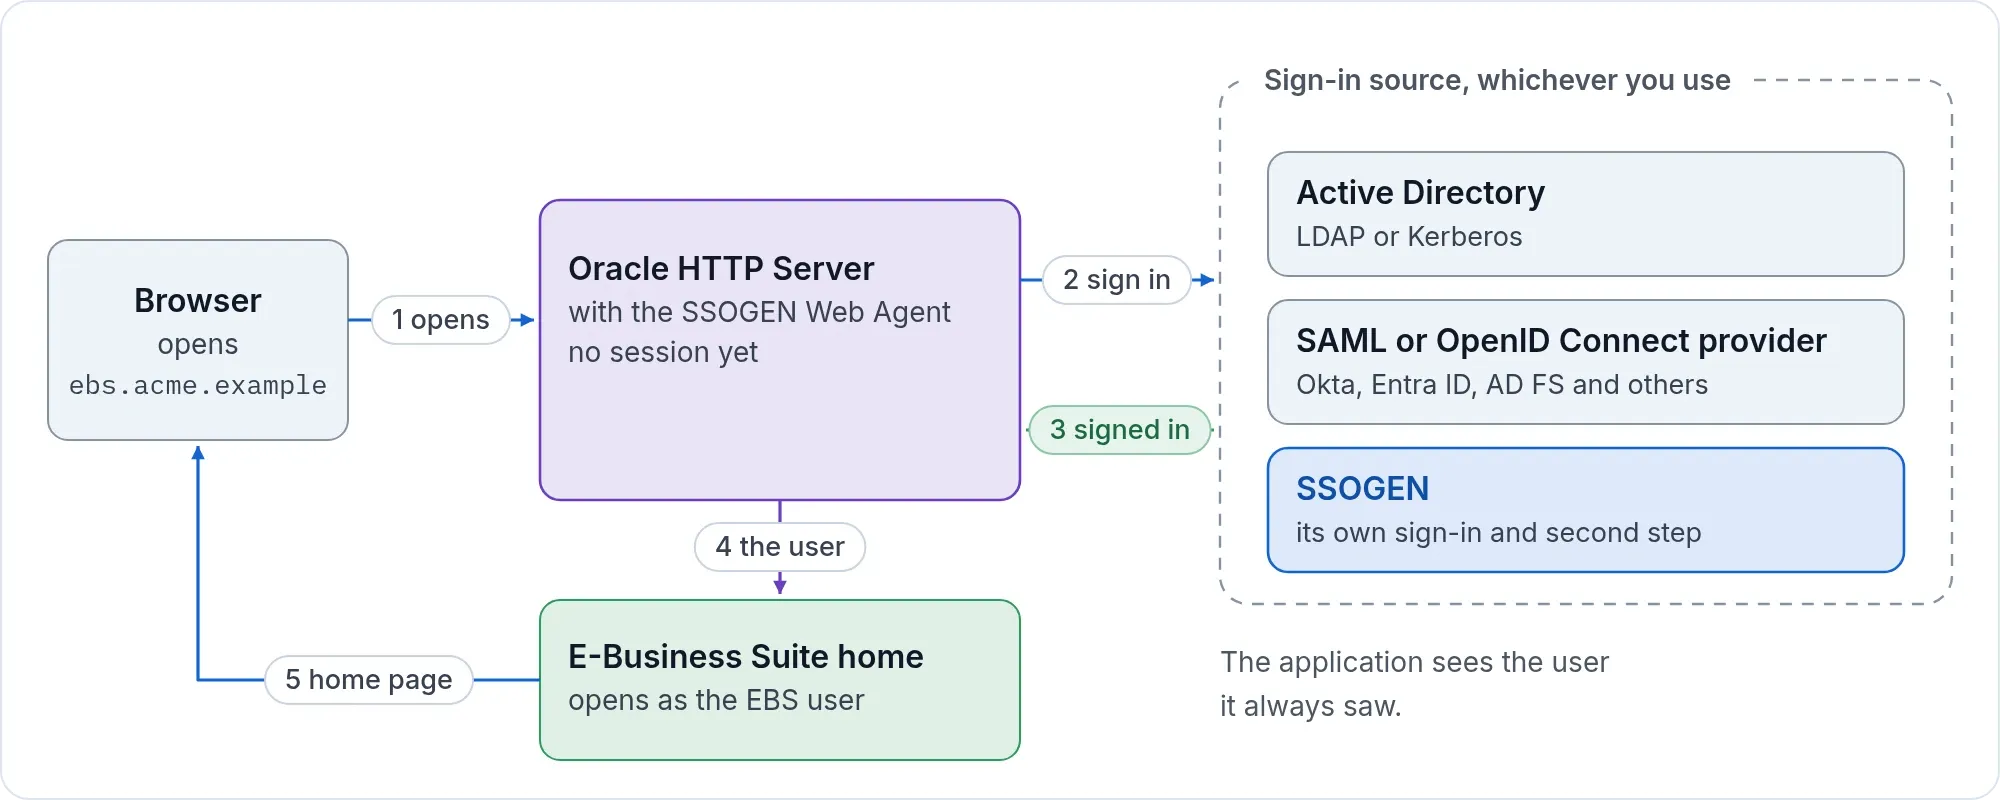
SSOGEN is one more app integration in Okta, and it gives EBS the user name through Oracle's own single sign-on settings.
How a sign-in goes
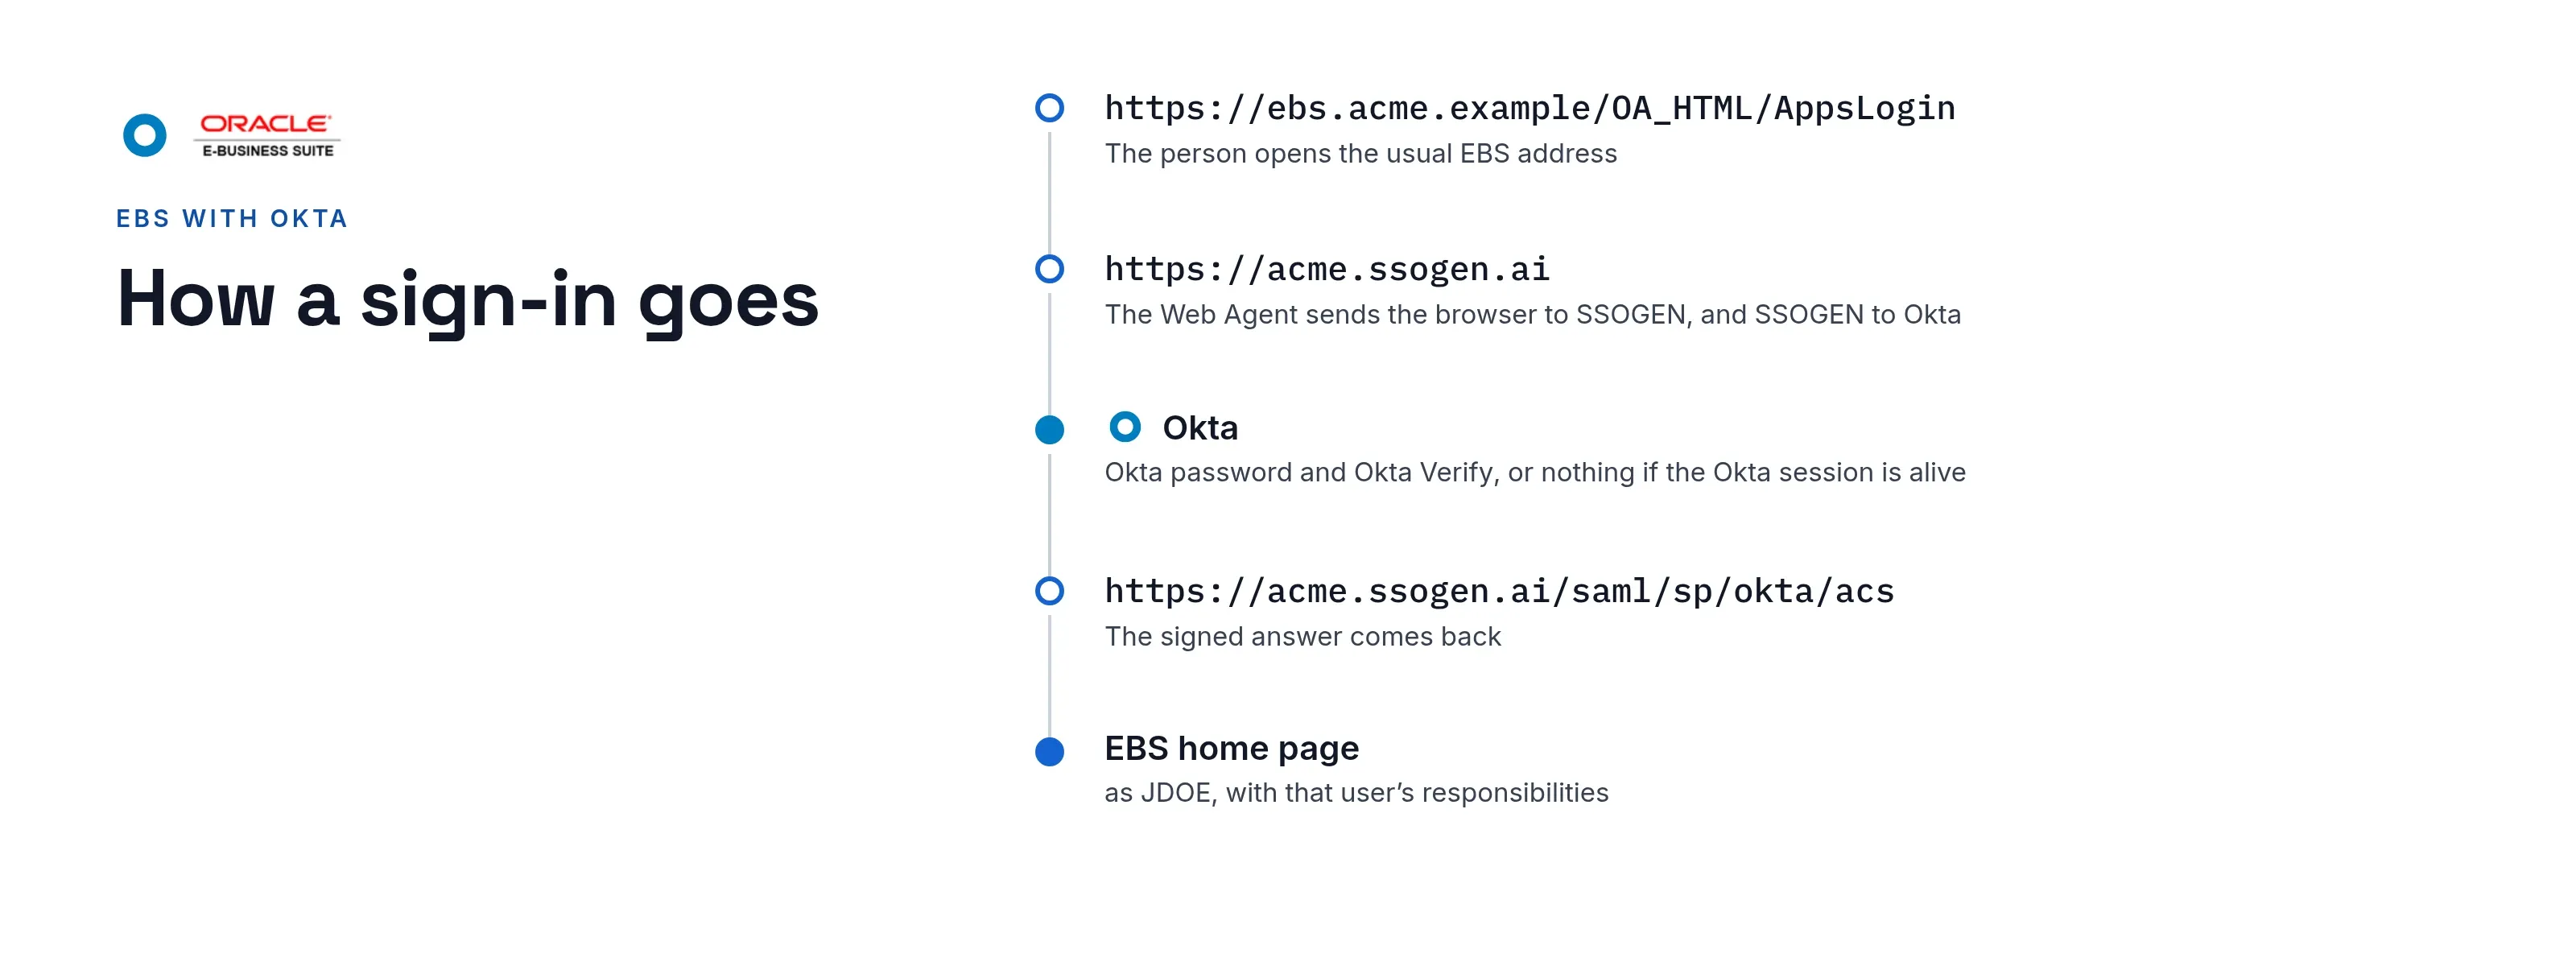
- A person opens
https://ebs.acme.example/OA_HTML/AppsLogin. - The SSOGEN Web Agent on the EBS web tier sends the browser to SSOGEN, and SSOGEN sends it to Okta.
- Okta signs the person in with whatever your org uses: a password, Okta Verify, a security key, or Windows integrated sign-in through an Okta Active Directory agent. There is no limit on Okta’s authentication policies, and EBS is covered by Okta MFA.
- The browser comes back to the EBS home page.
A person who already has an Okta session never sees a sign-in page. The Okta administrator can also put EBS on the Okta dashboard as a bookmark to the EBS address, and people launch it like any other Okta application.
No Oracle Access Manager, Oracle Internet Directory or Oracle Unified Directory is needed, and the same Okta setup serves PeopleSoft and JD Edwards.
What you need
- An Okta administrator who can create app integrations and assign people.
- Oracle E-Business Suite 12.2 or 12.1, and the SSOGEN integration tool for it.
- An SSOGEN tenant,
https://acme.ssogen.ai, or a license key for the direct path below.
Path A: through SSOGEN
In Okta
Create a SAML 2.0 app integration for SSOGEN, with the values SSOGEN shows:
| Okta field | Value |
|---|---|
| Single sign-on URL | https://acme.ssogen.ai/saml/sp/okta/acs |
| Audience URI (SP Entity ID) | https://acme.ssogen.ai/saml/sp/okta |
| Name ID format | Unspecified |
| Application username | Okta username or Email |
| Attribute statements | email = user.email, displayName = user.displayName |
| Assignments | The people or groups who may use EBS |
OpenID Connect works too (web application, authorization code, redirect URI https://acme.ssogen.ai/oidc/rp/okta-oidc/callback). Every field, the issuer and the Okta errors are on Okta as the sign-in source.
In SSOGEN
Fetch the Okta metadata, map email and displayName, then create, validate, test, try and activate the provider, and allow it in the policy that covers EBS.
On the EBS side
- Register EBS in SSOGEN as a Web Agent application with the Client URL
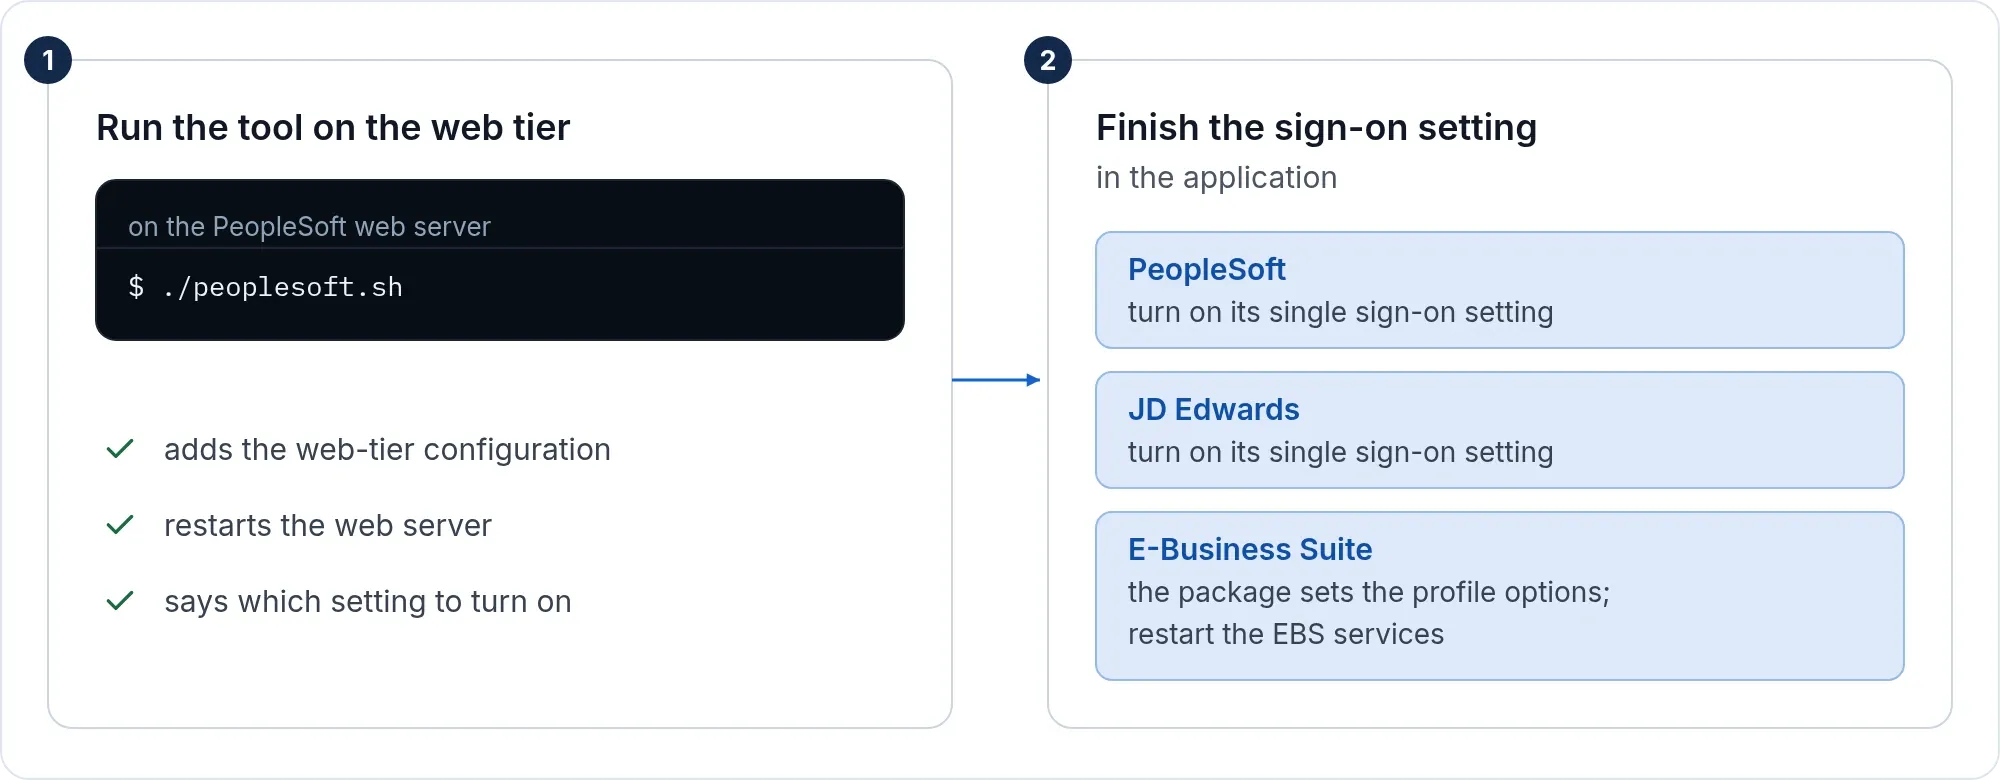
https://ebs.acme.example, and set Identify the person by to the value that equals the EBS user name. John Doe’s EBS userJDOEneedsjdoeorJDOE; the agent sends it in capitals and never cuts off a domain part, so an email address would not match. - Run the tool and finish the setting in EBS as on the Oracle EBS single sign-on page.
- Create the EBS users. EBS links the account at the first sign-in. Keep
https://ebs.acme.example/OA_HTML/AppsLocalLogin.jspforSYSADMIN.
Path B: straight to Okta, no SSOGEN in between
With a license key from SSOGEN, the tool connects the EBS web tier to Okta directly.
SAML (-mode=saml). In Okta create a SAML 2.0 app integration:
| Okta field | Value |
|---|---|
| Single sign-on URL | https://ebs.acme.example/ssogen/acs |
| Audience URI (SP Entity ID) | https://ebs.acme.example |
| Application username | A value that equals the EBS user name, such as the Okta username when it is jdoe |
| Assertion Signature | Signed |
Save the metadata as ebs-internal-idp.xml in the ssogen folder, or set SSOGENSamlIdpMetadataURL, and run the tool as on the EBS page.
OpenID Connect (-mode=oidc). Create a web application with the redirect URI https://ebs.acme.example/ssogen/oidc/callback, give the tool the client ID and SSOGEN_OIDC_SECRET, and set SSOGENOidcProviderMetadataURL to https://<your Okta domain>/.well-known/openid-configuration.
If it does not work
| Symptom | What to do |
|---|---|
| Okta says the user is not assigned to the application | Assign the person or group on the Assignments tab. |
| Try connection says the assertion was addressed to a different service provider | The Audience URI differs from the entity ID in use. Paste it again. |
Okta complains about redirect_uri |
The redirect URI is not in Sign-in redirect URIs exactly as shown. |
| Sign-in works, EBS does not know the user | The name sent is not an EBS user name. Change Identify the person by, or the Application username in Okta. |
| Sign-ins stop after a certificate change in Okta | Fetch the metadata again and activate it before you make the new certificate active. |