SSOGEN / CyberArk alternative for AI agent identity and just-in-time server access
Compare
CyberArk alternative for AI agent identity and just-in-time server access
SSOGEN is a CyberArk alternative for three jobs: an owned identity for every AI agent and service, just-in-time access to servers with an approver, and browser sessions over SSH, RDP and VNC. It is an identity provider with a Gateway, not a password vault, and it signs people in to applications from the same console.
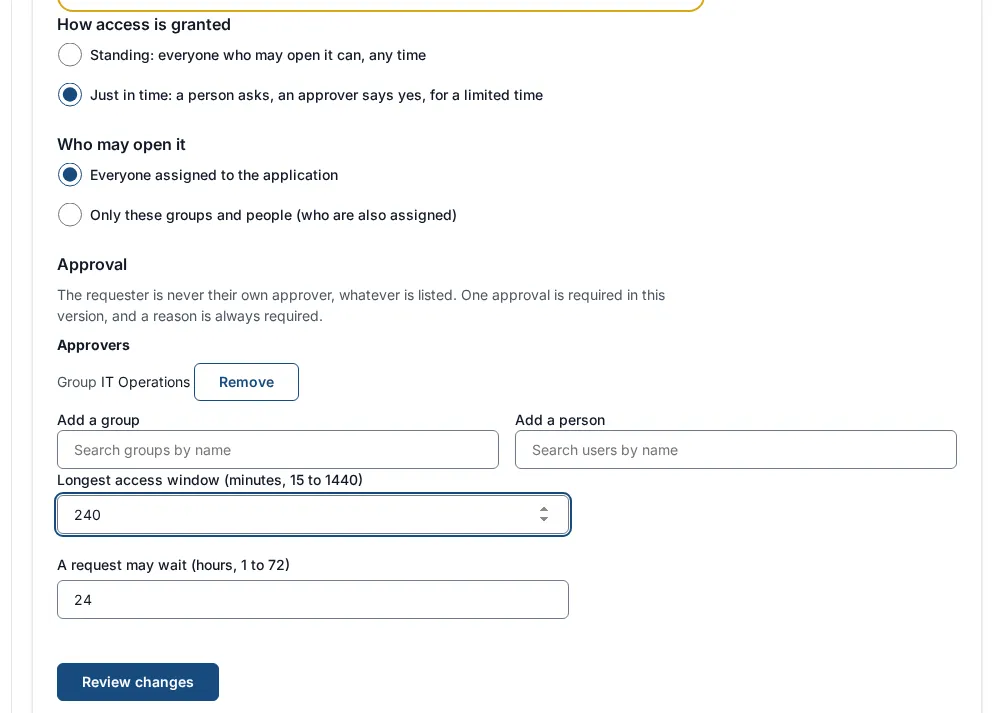
A Remote Access resource in SSOGEN: standing access, or just in time with an approver and a time limit.
The right CyberArk alternative depends on which CyberArk job you are filling. CyberArk’s products now appear as Idira from Palo Alto Networks. SSOGEN covers identity for AI agents and other non-human callers, and approved, time-limited access to servers. It signs people in to applications from the same console.
Which CyberArk job is this?
| Job | Idira (CyberArk), in its own words | SSOGEN |
|---|---|---|
| Vault and rotate privileged accounts | “Protect critical system-level accounts with automated credential vaulting and rotation” | Remote Access keeps one write-only account per server, released to the Gateway for one session and only to a host that proved its identity. An administrator replaces it on the host and in SSOGEN |
| Isolate and record sessions | “Isolate and record every sensitive session across infrastructure and SaaS” | SSH, RDP and VNC run in the browser through the Gateway. Every session is recorded as events: who, which host, why, when, the host identity, clipboard use and file transfers by size and digest |
| Just-in-time access | “Just-in-Time entitlements that replace static, long-lived IAM roles” | A person asks with a reason, one approver says yes, and the window lasts 15 minutes to 24 hours |
| AI agents | “Idira Secure AI Agents scans SaaS, cloud and developer environments to identify active agents” | Each agent is registered with owners, a key pair, granted scopes and an expiry; the MCP Gateway checks every tool call |
| Secrets for workloads | “Modern secrets management, including governance and reporting for all vaults and workloads” | Not covered by this comparison |
| Workforce sign-in | Not covered by this comparison | A complete identity provider: SAML, OpenID Connect, MFA and the Web Agent for Oracle applications |
Idira facts come from Palo Alto Networks’ Idira pages, where CyberArk product links now lead, read 2026-11-15.
Just-in-time access to a server, step by step
Ask
Maria Lopez opens My Apps, selects Request access on Acme Build Server (SSH), and gives a reason of 10 to 500 characters and a duration.Approve
An approver listed on the resource decides from their own Approvals page. The approver needs a second sign-in step from the last 10 minutes, and nobody can approve their own request.Open
Inside the approved window, Maria opens the host in the browser. The session also ends at the resource’s maximum session or idle timeout.End
When the window ends, or a Super admin revokes the access, the live session is ended. Every request, decision and session event lands in the audit trail.
The full setup is in approvals and access windows, and the product view is on secure remote access.
AI agents and other non-human identities
SSOGEN calls these records non-human identities, in four types: AI agent, MCP client, Automation and Service.
- An owner for every agent. Up to five people own each agent. If the last owner leaves, the agent is suspended.
- No passwords for agents. An agent proves itself with a key pair, and every token is bound to that key and lives about four minutes.
- Consent when it acts for a person. The person approves the scopes and a duration of at most 30 days, and can withdraw it in My Account.
- A human decision for sensitive scopes. A scope marked Sensitive needs a fresh approval each time.
- A stop button. Suspend one agent, revoke it, or engage a kill switch for a whole agent type.
- Per-tool-call checks. The MCP Gateway authorizes each tool call against the agent’s granted scopes.
The model is explained in depth on AI agent identity.
Questions people ask
What is the best open-source PAM solution?
How much is CyberArk?
What is CyberArk now called?
Does CyberArk do secrets management?
Where to go next
- All comparisons. The SSO comparison hub lists each product SSOGEN is compared with.
- Workload identity. The Aembit alternative compares workload and agent access.
- Session audit. Remote Access session audit lists every fact SSOGEN records.
Sources, all read 2026-11-15: Idira privileged access management, the target of CyberArk’s Privileged Access Manager link; Idira overview, the target of CyberArk’s Secure AI Agents link.
CyberArk is a trademark of CyberArk Software Ltd. Idira and Palo Alto Networks are trademarks of Palo Alto Networks, Inc. SSOGEN is not affiliated with either company. Competitor details are from their public pages and may change; check them for your own subscription.