SSOGEN / Okta alternative: SSOGEN and Okta compared
Compare
Okta alternative: SSOGEN and Okta compared
Both are SAML and OpenID Connect providers; they differ in how they reach Oracle and other on-premises applications, in server access and in where they run.
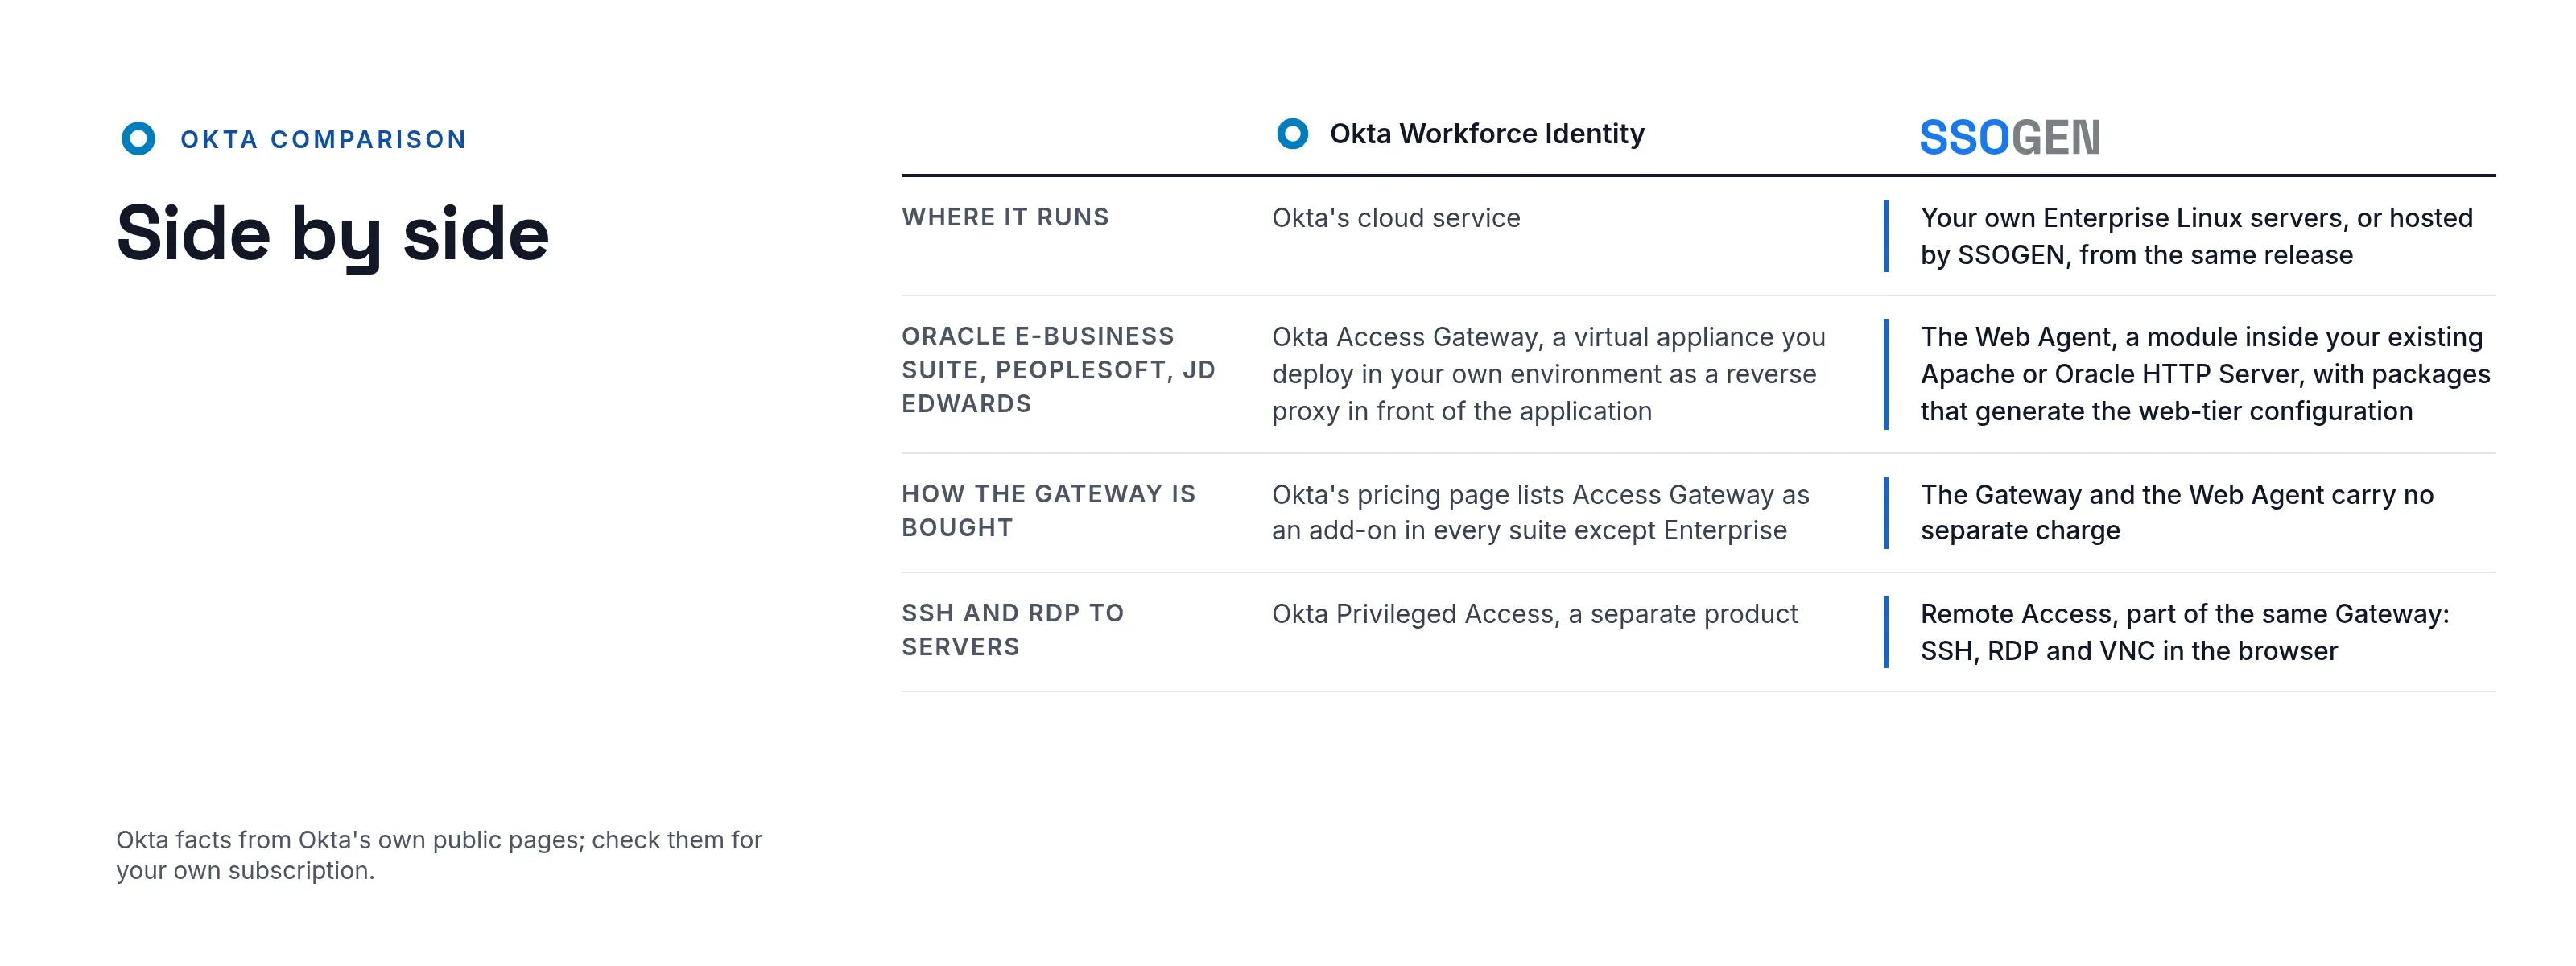
Side by side
| Okta Workforce Identity | SSOGEN | |
|---|---|---|
| Where it runs | Okta’s cloud service | Your own Enterprise Linux servers, or hosted by SSOGEN, from the same release |
| SaaS applications | A catalog of thousands of pre-built integrations | An app gallery in the console, and any SAML application or any OpenID Connect application that supports PKCE |
| Oracle E-Business Suite, PeopleSoft, JD Edwards | Okta Access Gateway, a virtual appliance you deploy in your own environment as a reverse proxy in front of the application | The Web Agent, a module inside your existing Apache or Oracle HTTP Server, with packages that generate the web-tier configuration; or the SSOGEN Gateway as a reverse proxy |
| How the gateway is bought | Okta’s pricing page lists Access Gateway as an add-on in every suite except Enterprise | The Gateway and the Web Agent carry no separate charge |
| SSH and RDP to servers | Okta Privileged Access, a separate product | Remote Access, part of the same Gateway: SSH, RDP and VNC in the browser |
| Phone app | Okta Verify | SSOGEN Authenticator, with number matching that cannot be switched off |
| Access decisions | Policies, including risk-based options | Readable policies with a What if screen; no AI model in the decision |
Okta facts come from Okta’s own public pages: the pricing page, the Okta Integration Network, and the Access Gateway documentation (supported application types and deployment). Check them for your own subscription.
Where Okta is strong
- The catalog. Thousands of pre-built SaaS integrations. If your estate is mostly SaaS, that matters.
- Oracle coverage through its gateway. Okta Access Gateway documents application types for E-Business Suite, PeopleSoft, JD Edwards, Hyperion and other Oracle products.
- A desktop authenticator. Okta FastPass offers device-bound, phishing-resistant sign-in on laptops.
Where SSOGEN differs
- Inside the web server you already run. The SSOGEN Web Agent loads into Apache 2.2, Apache 2.4 or Oracle HTTP Server, so there is no extra virtual appliance in the request path for those applications. For other applications, the SSOGEN Gateway publishes them as a reverse proxy.
- Nothing to enroll on the application server. The console generates a short configuration block with a key for one application; the application team pastes it. They hold no SSOGEN account.
- One product for sign-in, internal web apps and servers. App Proxy and browser SSH, RDP and VNC share the console, policy and audit trail with every other sign-in.
- Self-hosted when you need it. All of SSOGEN runs on your servers, with your database, your signing keys and your audit trail.
Moving from Okta
Teams comparing Okta alternatives ask one question first: can we move without a flag day? Okta can stay the sign-in source while applications move to SSOGEN one at a time.
| What you carry over | How SSOGEN takes it |
|---|---|
| People and groups, kept current during the cutover | Okta provisions into SSOGEN’s SCIM 2.0 endpoint with a bearer token you issue and revoke per client. Deactivation by PATCH active=false disables the account, and externalId round-trips, so a re-sync creates no duplicates |
| Passwords people already know | A CSV import takes an optional password_hash column: bcrypt, SSHA-512, SSHA-256 or PBKDF2 (SHA-256 or SHA-512). Those people are not asked to reset, and each hash is replaced with Argon2id at the first successful sign-in |
| Group rules | A group’s membership can follow a rule: everyone, an email domain, or the sign-in connection a person came from |
| Nested groups | A group can contain other groups, and membership counts through every level |
| Event hooks | Webhooks send the audit events you choose, signed with HMAC-SHA256 over the timestamp and body, retried in order |
| Provisioning to SaaS apps | Outbound provisioning creates the people assigned to any application with a standard SCIM 2.0 endpoint, directly or through groups |
| Okta itself, during the move | Okta stays an upstream OpenID Connect or SAML provider, so people keep signing in at Okta until you switch |
A file that holds plain text instead of a hash is refused whole, before anyone is created.
Okta, Okta Verify, Okta FastPass and Okta Access Gateway are trademarks of Okta, Inc. Oracle, E-Business Suite, PeopleSoft and JD Edwards are trademarks of Oracle and its affiliates. SSOGEN is an Oracle partner, but Oracle has not reviewed or endorsed this page. SSOGEN is not affiliated with Okta. Competitor details are from their public pages and may change; check them for your own subscription.