SSOGEN / Oracle EBS SiteMinder single sign-on with SSOGEN
Integration
Oracle EBS SiteMinder single sign-on with SSOGEN
Keep SiteMinder as the SAML sign-in source, let SSOGEN check the same directory itself, or replace SiteMinder, with no Oracle Access Manager in any of them.
Choose the way
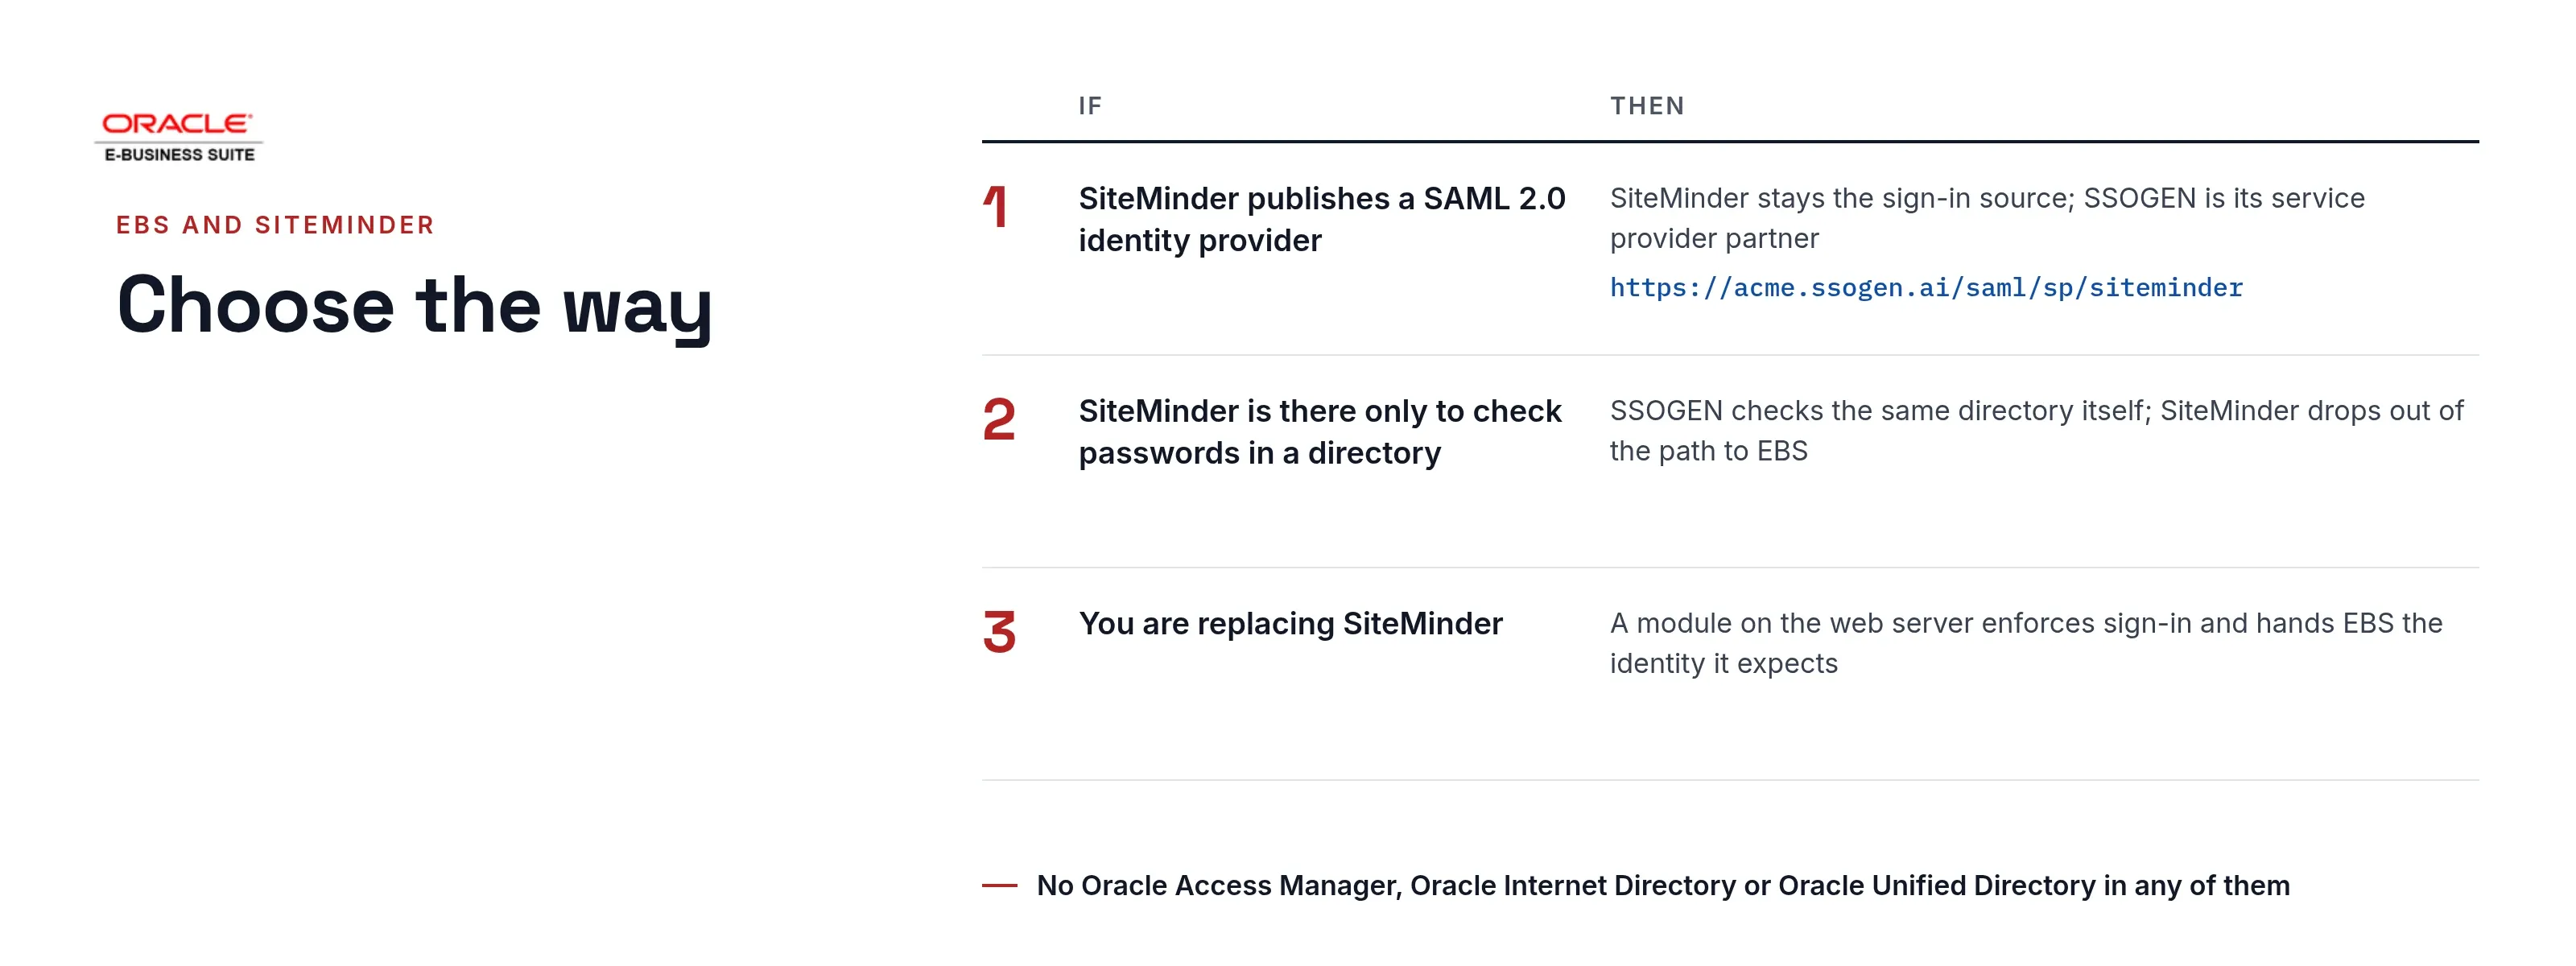
| If | Then |
|---|---|
| SiteMinder publishes a SAML 2.0 identity provider (its federation service) | SiteMinder stays the sign-in source and SSOGEN is registered with it as a service provider: Path A. |
| SiteMinder is there only to check passwords in a directory | SSOGEN checks the same directory itself: Active Directory and LDAP. SiteMinder drops out of the path to EBS. |
| You are replacing SiteMinder | See migrating from legacy access managers: a module on the web server enforces sign-in and hands EBS the identity it expects, and the application does not change. |
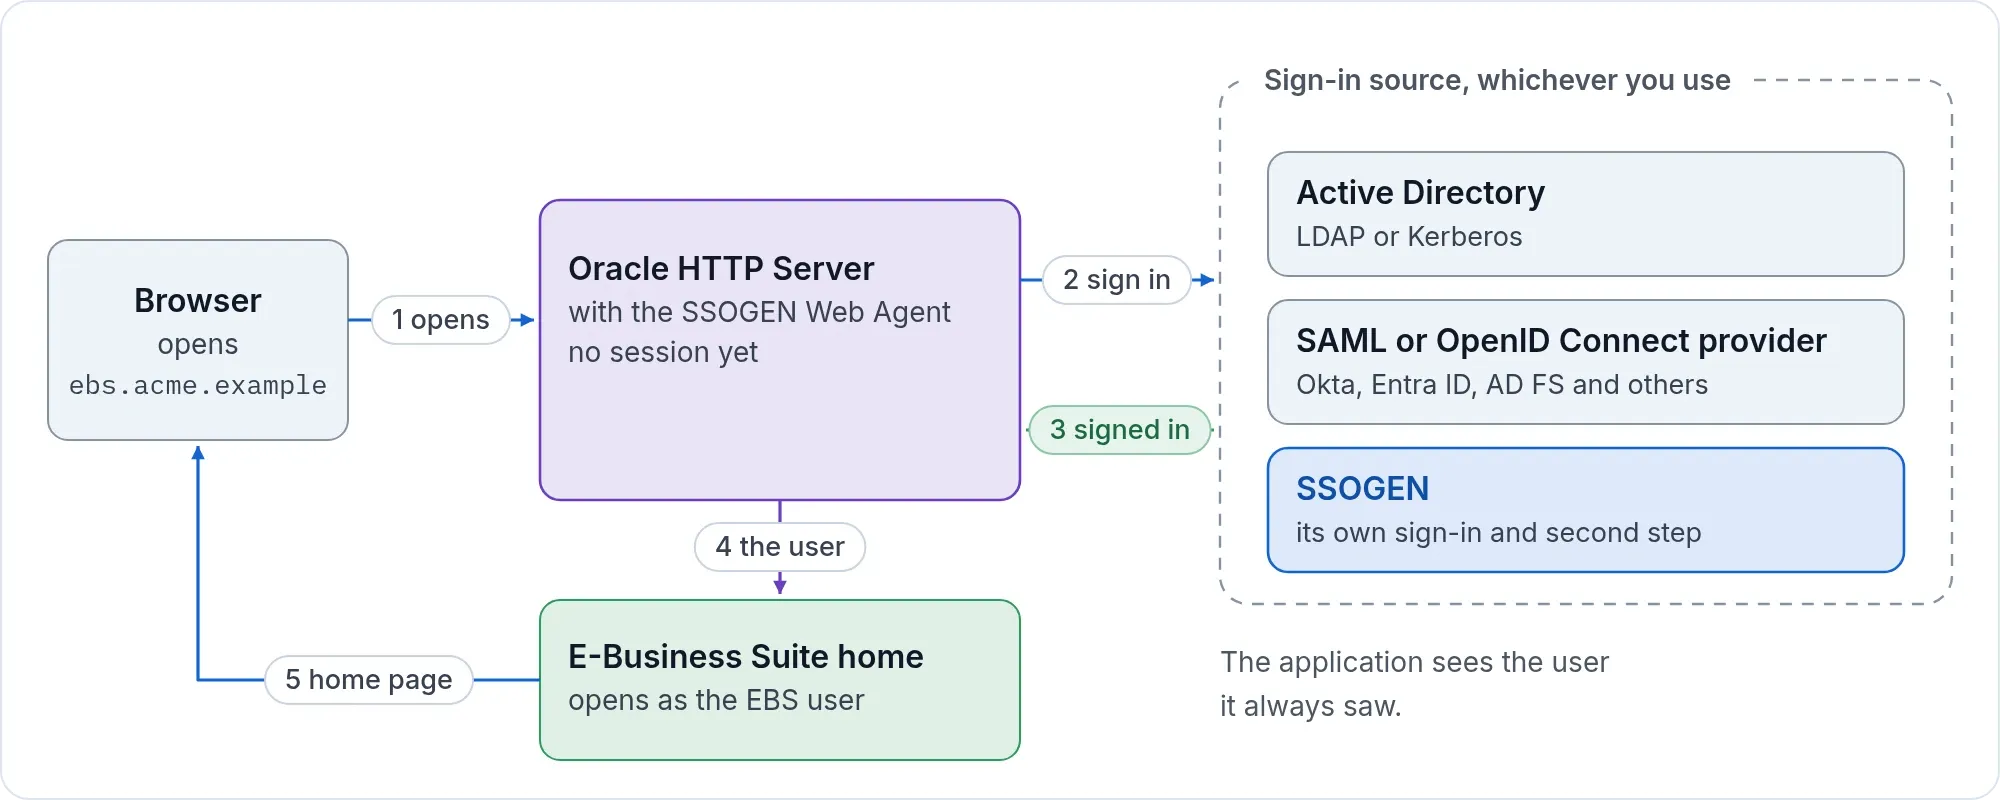
Users keep one sign-in. Someone who already signed in at SiteMinder reaches EBS without another prompt, and with the SAML path opening EBS from other SiteMinder-protected applications works the same way, as long as SiteMinder’s session is alive.
Path A: SiteMinder as the SAML sign-in source
In SiteMinder
Register SSOGEN as a service provider partner of your SiteMinder SAML 2.0 identity provider:
| SiteMinder asks for | Value |
|---|---|
| Service provider entity ID | https://acme.ssogen.ai/saml/sp/siteminder |
| Assertion consumer service URL, HTTP-POST | https://acme.ssogen.ai/saml/sp/siteminder/acs |
| Assertion | Signed; a stable Name ID; the email address as mail |
What the provider must send is on Any SAML identity provider.
In SSOGEN
Import SiteMinder’s IdP metadata, map the attributes, then create, validate, test, try and activate the provider and allow it in the policy that covers EBS (Add a SAML identity provider in SSOGEN).
On the EBS side
- Register EBS in SSOGEN as a Web Agent application with the Client URL
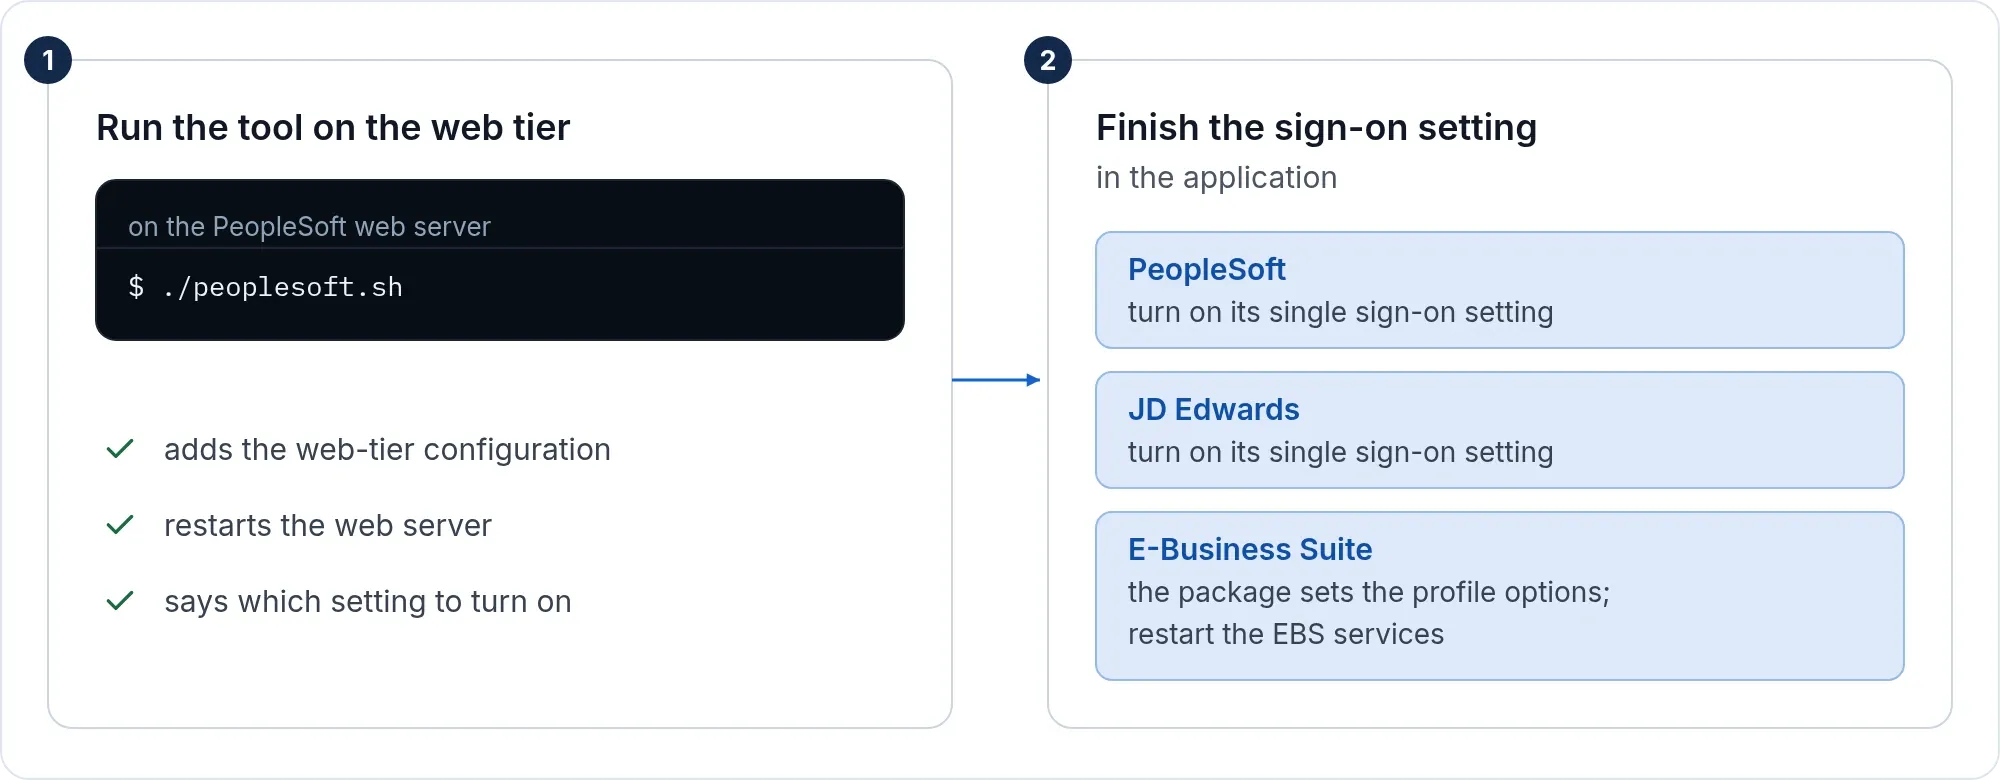
https://ebs.acme.example, and set Identify the person by to the value that equals the EBS user name:jdoeorJDOEfor the EBS userJDOE. The agent sends it in capitals and never cuts off a domain part. - Run the tool and finish the setting in EBS as on the Oracle EBS single sign-on page: Applications SSO Type
SSWA w/SSO,APPS_AUTH_AGENThttps://ebs.acme.example/accessgate, Login TypesBoth. - Create the EBS users; EBS links the account at the first sign-in. Keep
https://ebs.acme.example/OA_HTML/AppsLocalLogin.jspforSYSADMIN.
Path A, direct
With a license key the tool connects the EBS web tier to SiteMinder’s SAML IdP without SSOGEN in between (-mode=saml): entity ID https://ebs.acme.example, ACS URL https://ebs.acme.example/ssogen/acs, Name ID equal to the EBS user name, IdP metadata saved as ebs-internal-idp.xml. See the EBS page.
If it does not work
| Symptom | What to do |
|---|---|
| “The assertion carried no subject (NameID)” | The partnership sends no Name ID. Configure one. |
| “That metadata publishes no signing certificate” | Export the IdP metadata with its signing certificate. |
| Sign-in works, EBS does not know the user | The name sent is not an EBS user name. Change Identify the person by or the Name ID. |